


The Feinwerk Connector is now in the Matomo Marketplace. Install it right inside Matomo, no download, no FTP. Read the news · Here is how →
One login. The right permissions. Always current.
Auth SAML connects Matomo to your identity provider: SAML 2.0 single sign-on, SCIM 2.0 on- and offboarding and site permissions driven by your IdP groups. For Okta, Microsoft Entra ID, Keycloak and any SAML provider.
from €1,299/year · cancel any time
Latest v5.1.2 · Matomo ≥ 5.0.0
One login for everything
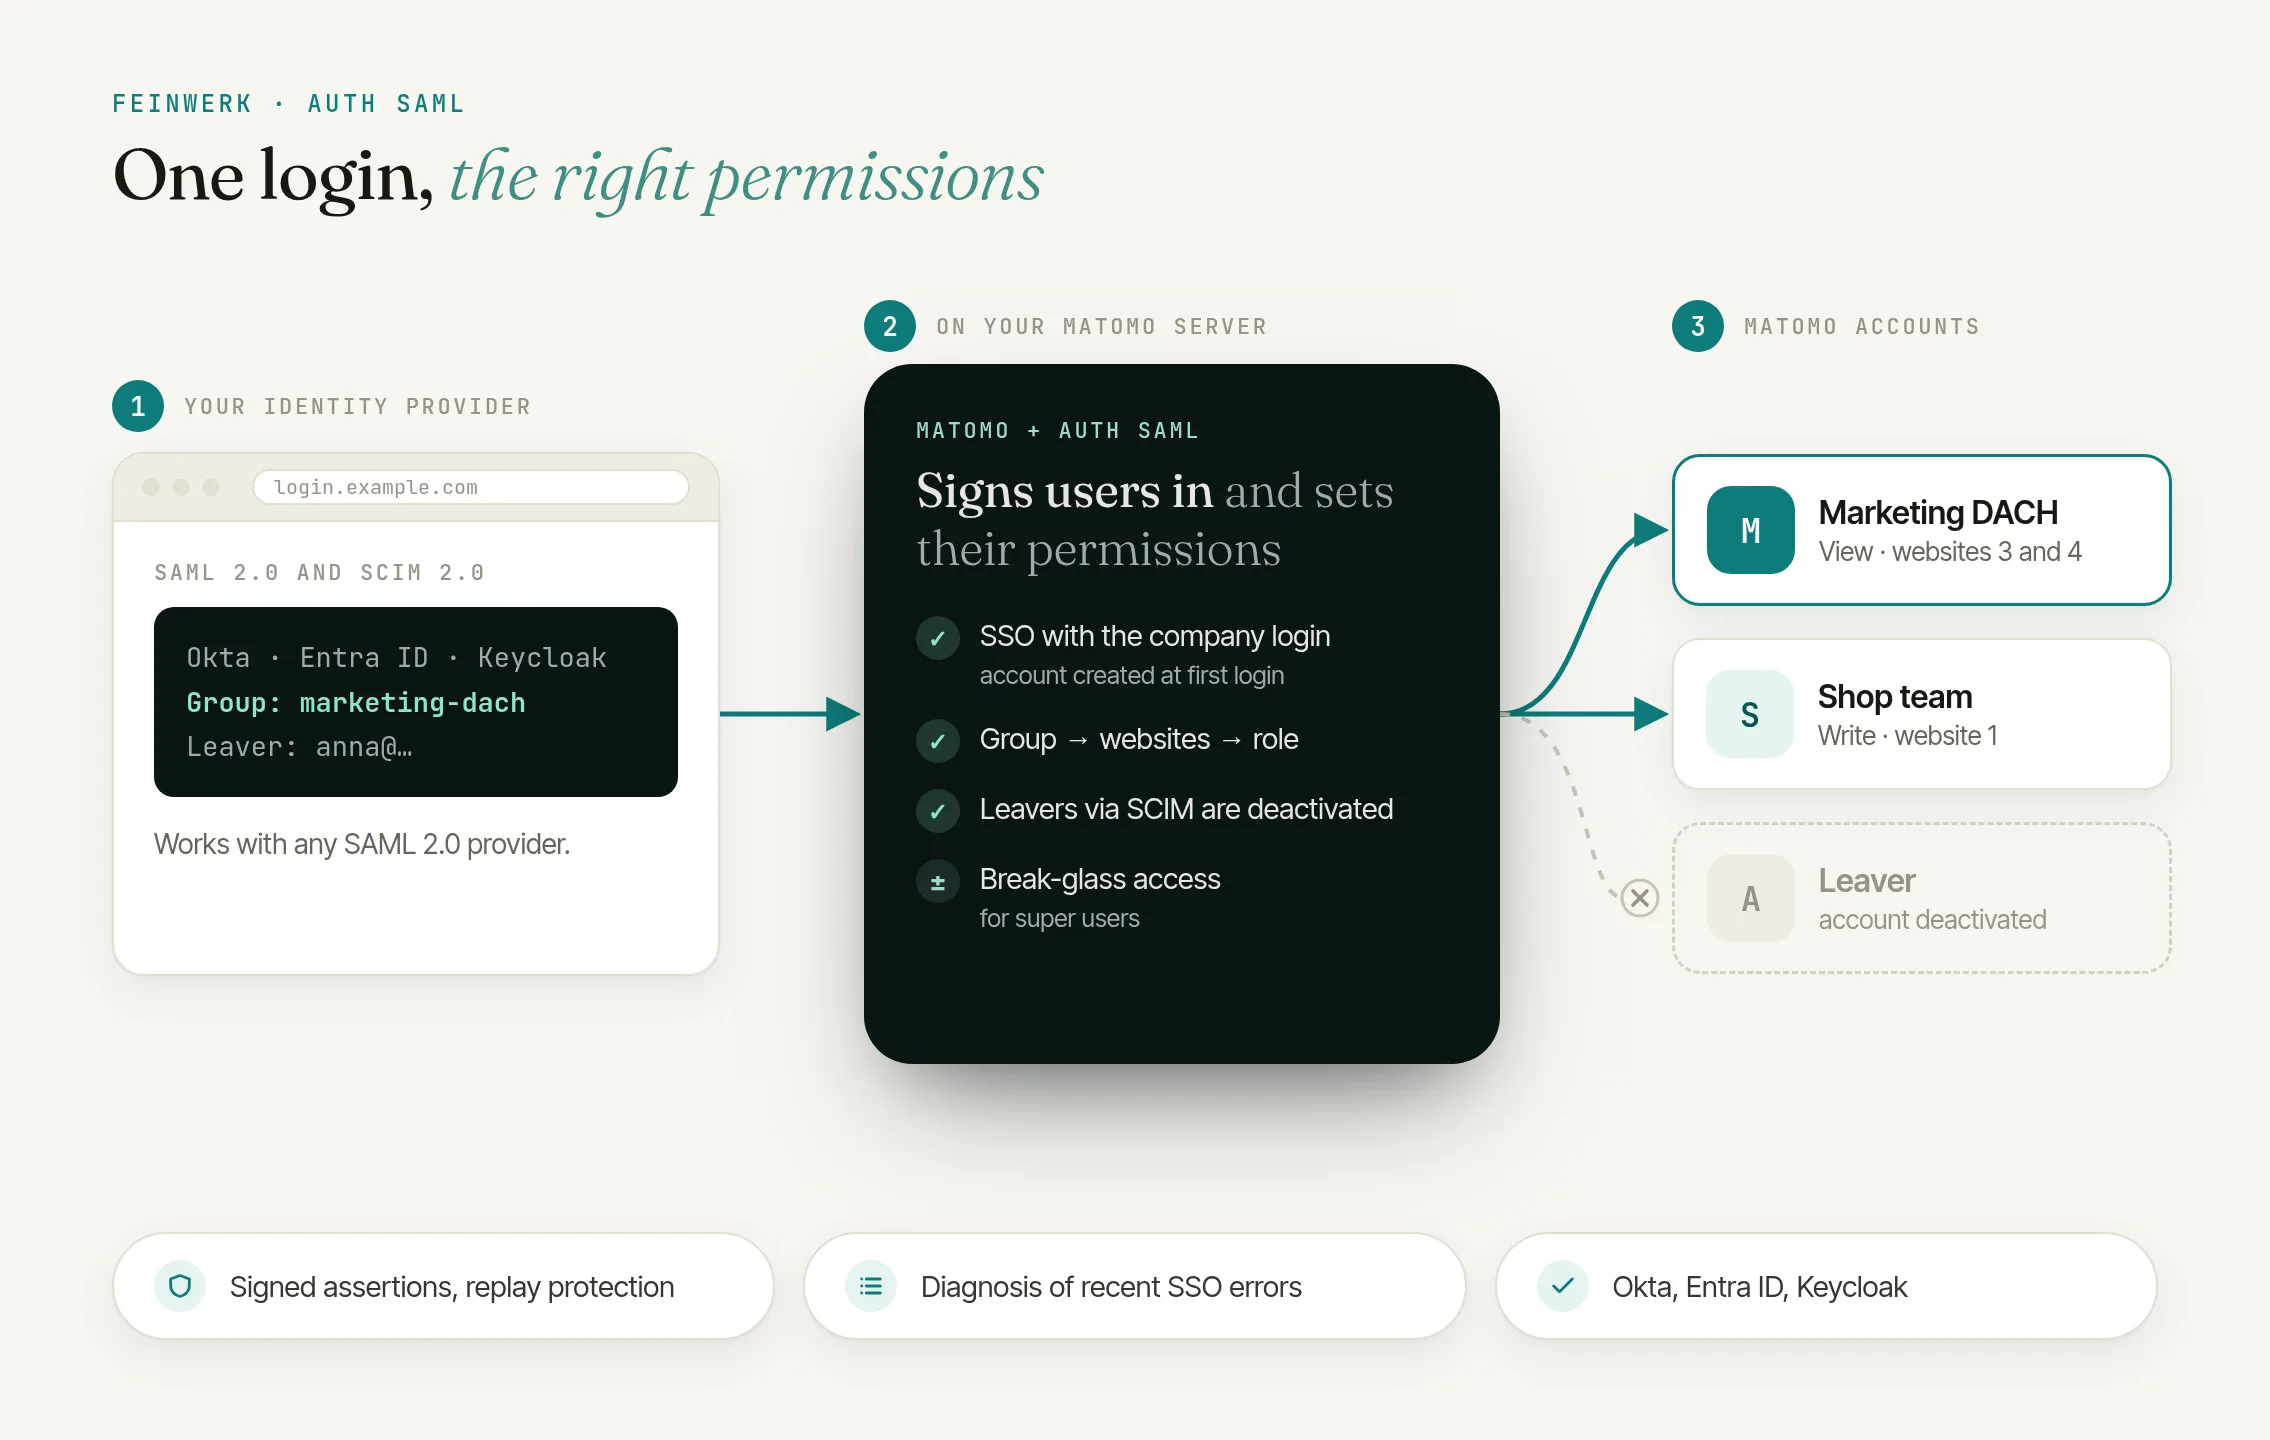
Your users sign in with their company account, SP- or IdP-initiated, optionally with single logout and Force SSO. Accounts are created automatically on first login.
Permissions from IdP groups
Group → sites → role: the mapping in the admin area turns your IdP into your access management. Permissions sync on every login and every SCIM change, and manually assigned permissions stay untouched if you want.
Real-time offboarding
As soon as your IdP reports a leaver via SCIM 2.0, Auth SAML deactivates the account: sessions end and the permissions the plugin granted are revoked. No login involved, no manual cleanup.
No lockout risk
Strict mode, signed assertions and replay protection are the defaults. Yet by default, super users keep a break-glass password login, so an IdP outage does not lock you out of Matomo.
Security you can prove
An audit log records SSO logins as well as account, permission and configuration changes, with CSV export. If you wish, Matomo requires multi-factor sign-in at the identity provider, SSO users confirm sensitive actions there instead of with a Matomo password, and an email arrives before a certificate expires.
Test instead of guessing
The SSO test on the admin page shows in advance what your identity provider sends and which account with which permissions a login would give, without signing anyone in. If a login fails later, the admin page shows why, including the groups and attributes received.
Click to enlarge
- License for 1 Matomo instance + 3 test instances, all websites and users
- Prices incl. VAT, billed via Paddle
- 14-day trial, cancel before it ends at no cost
- Updates and support included
- Refunds
Matomo single sign-on through your identity provider, with permissions from IdP groups
Your team signs in to Matomo via SAML with Entra ID, Okta or Keycloak, and permissions come straight from your identity provider's groups.
Read the use case →Any SAML 2.0 compliant IdP. Auth SAML is tested with Okta, Microsoft Entra ID and Keycloak. GitHub does not offer SAML as an IdP, so use a brokering IdP such as Keycloak there.
No. Account creation and permission sync work entirely through the SAML login (just-in-time). SCIM is worth it when offboarding must take effect immediately instead of at the next login.
Yes. In the default "managed" mode, Auth SAML only revokes permissions it granted itself, and everything assigned manually stays untouched. If you want the IdP as the single source of truth, choose the authoritative mode.
Super users still reach the password form through the break-glass login, even when Force SSO is on. You decide who else may sign in with a password: everyone, super users only (the default) or nobody. If you switch password login off completely, the break-glass login is blocked too. The setting can then be reset on the command line.
No. Before sensitive actions such as creating an API token they confirm by signing in at the identity provider again, and Matomo's own two-factor prompt is skipped for SSO logins, since the sign-in happens at the identity provider. Both can be changed in the settings.
Manageable: register the SP metadata URL in your IdP, paste the IdP metadata URL into the plugin (automatic import with daily refresh) or upload the metadata file, create your group mappings. The SSO test on the admin page shows what arrives before you switch over. Step-by-step guides for Okta, Entra ID and Keycloak are in the documentation.
Only if you explicitly enable it and define a dedicated IdP group. If the group later disappears from the claim, Auth SAML removes the super user rights it granted itself. Super users the plugin did not appoint are never demoted, and neither is the last super user.
They are adopted, not duplicated: on the first SSO login, Auth SAML matches the account by login or email address and links it to the IdP permanently. The password is kept, and manually assigned site permissions stay untouched in the default mode, because the plugin only ever revokes what it granted itself. By default, Auth SAML does not adopt super user accounts automatically, so no IdP account can take over the local emergency access, and existing super users are never demoted. SCIM provisioning adopts existing accounts the same way, so you can introduce SSO on a running Matomo installation without recreating users or losing permissions.
Because it covers more: beyond SAML sign-in, Auth SAML includes permission management through IdP groups and a full SCIM 2.0 server for automatic on- and offboarding. One license replaces manual user administration across the entire lifecycle.
- 01 Install the Feinwerk Connector from Matomo's Marketplace: under Administration › Platform › Marketplace, search for "Feinwerk", install and activate it. Without the Marketplace: download the ZIP.
- 02 Open Feinwerk Plugins and click "Connect with Feinwerk account". If your browser cannot reach the store, enter your instance token in the connector settings instead.
- 03 Open the Feinwerk Plugins screen, find Auth SAML, and click Install.
Prefer a manual install? After the purchase you will find the ZIP download in your customer account. · Documentation for Auth SAML
Missing a feature in Auth SAML? Tell us what you need →
Auth SAML
Auth SAML turns your identity provider into the single source of truth for Matomo: sign-in via SAML 2.0 single sign-on, user lifecycle via SCIM 2.0, and site permissions driven by your IdP groups. It works with any SAML 2.0 provider and is tested with Okta, Microsoft Entra ID and Keycloak.
Sign-in and permissions from one source
On the first SSO login, Auth SAML creates the Matomo account automatically (just-in-time provisioning). On every login it synchronizes site permissions from the group claims: in the admin area you map IdP groups to Matomo sites and a role (view, write or admin). From then on, access is managed in your IdP alone. Alternatively or additionally, Auth SAML reads permissions from a direct attribute (e.g. matomo_access = "view:1,4;write:2").
Three sync modes control how strictly the IdP leads: additive (only grants, never revokes), managed (revokes only what the plugin granted itself; manually assigned permissions stay untouched) or authoritative (the IdP fully defines permissions).
Offboarding that takes effect immediately
With SCIM 2.0 enabled, your IdP actively pushes users and groups to Matomo: new team members exist before their first sign-in. When the IdP reports that someone has left, Auth SAML deactivates the account right away: login is blocked, running sessions end and the permissions the plugin granted are revoked, with no one having to remember anything. Group changes in the IdP affect site permissions immediately, without any login involved.
Secure by default, with no lockout risk
Signed assertions, RSA-SHA256, strict mode and replay protection are the defaults. At the same time, Auth SAML is built so an IdP outage does not lock you out: super users reach the password form through a break-glass login, even when Force SSO is on. Login restrictions only apply once SAML is actually configured. Only if you switch off password login for everyone is the break-glass login blocked as well. By default, Auth SAML does not adopt super user accounts automatically via SSO or SCIM. If you wish, Matomo requires multi-factor sign-in at the identity provider, and SSO users confirm sensitive actions such as creating an API token by signing in there again. An audit log records logins and account, permission and configuration changes, and a security check points out weak settings.
Setup via metadata import
Copy the SP metadata URL into your IdP, paste the IdP metadata URL into the plugin: import and daily refresh are included, and certificate rollover at the IdP (e.g. Entra ID) is picked up automatically. If your server cannot reach the URL, upload the metadata file on the admin page. Before a certificate expires, your super users receive an email. Create your group mappings, done. The SSO test on the admin page shows before you switch over which groups and attributes arrive and which permissions follow from them, and the most recent SSO errors are listed there together with the groups and attributes actually received. No more guessing why a login fails. Console commands support automated rollouts, and step-by-step guides for Okta, Entra ID and Keycloak are in the documentation.
One license, the full lifecycle
Auth SAML is deliberately built as a complete solution: one license covers the entire user lifecycle, from SAML sign-in and permission management through IdP groups to SCIM provisioning with immediate offboarding. It replaces manual user administration and separate provisioning tools.
-
v5.1.2 Nov 13, 2026
- Security: when linking existing accounts through SSO and SCIM, the plugin compares login, e-mail address and NameID more strictly. An account whose login differs only in accents is no longer adopted, and an adopted account keeps the spelling of its login.
- Improved: saving the settings only adds an audit log entry for the metadata import when the import changed something.
- New: the bundled documentation describes which data the plugin stores and transmits, and names the included libraries with their licences.
v5.1.1
- Security: an SSO login started through Matomo now only counts in the browser in which it was started, so nobody can slip a login into another person's browser. The new setting "Bind the login to the browser" is on by default and works when Matomo is reached over HTTPS.
- New: the security check points out when this binding is switched off or Matomo is not reached over HTTPS.
- Improved: the feedback question at the end of the admin page now sits quietly in one line, with the support link at the end. The note on further Feinwerk offers is gone.
v5.1.0
- New: SSO test on the admin page. You see which attributes, groups and sign-in method arrive from the identity provider and which account with which permissions a login would give, without signing anyone in or changing anything.
- New: SSO users confirm sensitive actions by signing in at the identity provider again instead of with a Matomo password. SSO users can now create API tokens, too.
- New: Matomo's two-factor authentication is skipped for SSO logins, since the identity provider handles the sign-in (can be switched off).
- New: If you wish, Matomo requires a specific sign-in method at the identity provider, for example multi-factor authentication.
- New: Audit log of SSO logins, account, permission, SCIM and configuration changes on the admin page, with CSV export and a configurable retention period.
- New: E-mail to the super users or chosen recipients before a certificate of the identity provider or of Matomo expires.
- New: Security check on the admin page and in the system check.
- New: The identity provider's metadata can also be pasted as XML or uploaded as a file.
- Improved: Existing super user accounts are no longer adopted automatically through SSO or SCIM (default), and super user rights from an IdP group are removed again once the group is missing.
- Improved: SSO accounts cannot change their own e-mail address or password (can be switched off).
- Improved: The password login policy applies to every login form and to creating API tokens.
- Improved: The identity provider's metadata URL must start with https.
- Improved: Characters Matomo does not allow in usernames are replaced for new accounts instead of stopping the login.
- Improved: Group mapping rows for the same group are merged, and the admin page asks before replacing or revoking the SCIM token.
- Fixed: An SSO user deleted in Matomo is created again at the next login. Unexpected errors show the SSO error page with a reference number.
v5.0.1
- The feedback question and tips now take a single compact line.
v5.0.0
- New version scheme: the edition for Matomo 5 now carries versions 5.x.
- The license check works with every version of the Feinwerk Marketplace Connector.
- At the end of the admin page you find a short feedback question and a direct line to our support. Your Matomo server sends the answer to Feinwerk without any personal data; it can be switched off in the configuration.
- Below it a subtle note on further Feinwerk offers, visible to administrators only, dismissible and can be switched off.
- The plugin now calls itself Feinwerk Auth SAML everywhere; you find its settings under System, General settings under this heading.
-
v2.2.1 Oct 15, 2026
- Security improvement: after sign-in the plugin only redirects to addresses of your Matomo instance.
- Importing IdP metadata by URL works with several query parameters, on save, in the daily refresh and in the API.
- The SSO button matches the sign-in button width.
- Group mappings list sites as "ID: Name".
- Relative redirect targets after sign-in are resolved correctly.
-
v2.2.0 Oct 13, 2026
-
v2.1.0 Oct 1, 2026